ABOUT
ID_IDENTIFIER: SWAYAM
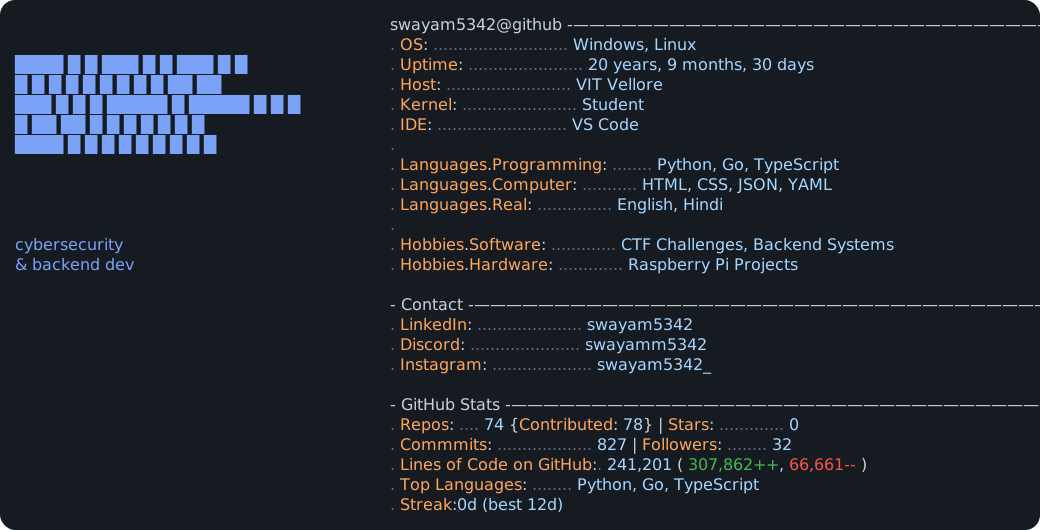
I build the invisible parts of software — APIs, deployment platforms, sandboxes, and detection pipelines — and I treat security as a design constraint, not a feature bolted on at the end.
I'm pursuing two degrees in parallel: a B.Tech in Cybersecurity at VIT Vellore and a BS in Data Science at IIT Madras. That mix shapes how I engineer — every system should be observable, measurable, and hard to break. Recent work includes a Kubernetes-native deployment platform (Kargo), a multi-tenant quality layer for MCP servers (PlugFit), a Linux sandboxing engine built on NsJail (Sandboxd), and a Windows SIEM pipeline with custom detection rules. Off the keyboard-shipping path, I reverse engineer binaries, dig into system internals, and tune detection logic for fun.
PRINCIPLES
- 01SECURITY IS AN INVARIANT, NOT A FEATURE.
- 02OBSERVABILITY IS PREREQUISITE FOR SECURITY.
- 03SIMPLICITY IS THE ULTIMATE HARDENING TOOL.
MAIN
CYBER
BACKEND
EXPERIENCE_JOURNAL
HISTORY_DUMPB.Tech in Cybersecurity
VIT Vellore
> Studying network security, cryptography, secure system design, operating systems, and vulnerability analysis while building practical backend and security systems.
BS in Data Science
IIT Madras
> Pursuing a parallel degree focused on statistics, machine learning, data structures, algorithms, and applied data science.
GITHUB_ACTIVITY
LIVE_STATS